SoylentNews is people
SoylentNews
Site News
Join our Folding@Home team:
Main F@H site
Our team page
Support us: Subscribe Here
and buy SoylentNews Swag
We always have a place for talented people, visit the Get Involved section on the wiki to see how you can make SoylentNews better.
- [day of the dalek] Alternative für Deutschland? I'm oKKK, you're oKKK.
- [c0lo] Eat well and exercise
- [Rich] ArtCraft
- [DannyB] Don't make Daylight Savings time permanent
- [mcgrew] False Propaganda
- [turgid] Runaway's Contentious Sig
- [linuxrocks123] Nonprofits in Capitalism
- [hubie] The Guardian Reviews AI Generated Sitcom
- [Runaway1956] More about GrapheneOS
- [Arthur T Knackerbracket] It’s OK To Tell ICE Their Actions Will Haunt Them, Judge Rul
- [Ingar] The devil is in the router
- [fliptop] FAFO
- [khallow] Evolutionary also-rans
- [bzipitidoo] How copyright warped Earthsea
- [istartedi] Forget the politics. Let's get back to our roots.
Older Stuff
-
Friday October 30 -
Thursday October 29- The Most Popular Streaming Platforms in the US Might Not be What You Think (11)
- Patrick Stewart Dies: ‘Star Trek: The Next Generation’ Actor Was 86 (34)
- Finland vs Google Treepocalypse (15)
- What in-House Legal Leaders Really Think About AI, in Their Own Words (16)
- Auto Tech Startup Claims It Traced Hack Attempt Back To Rival's IP Address (2)
- No Company Besides the Biggest Tech Giants Is Seeing Benefits From AI (42)
-
Wednesday October 28- Australia Ponders Robotaxi Introduction as Unions Bark Warnings (3)
- Human Receives AI-Designed Virus for the First Time (4)
- US Official: Russia's Stalker Satellite Sure Looks Like an Orbital Weapon (9)
- Walter Koenig, Actor Best Known as Chekov on Star Trek, Dies Aged 90 (21)
- Anthropocene: Rejection Revisited (9)
Quick Links

Late last week there was a hacking attack which initially stole $6.3B:
Binance targeted in $6.3 billion crypto heist, the largest ever
The company has suspended all deposits and withdrawals while it works with law enforcement to secure its infrastructure and locate stolen funds.
Its initial investigation pointed to a compromised laptop belonging to a DevOps engineer, which may have given the hacker access to an internal service and allowed them to submit unauthorized withdrawals.
Blockaid CEO Ben-Natan said in a statement to CoinDesk that "the tactics and level of sophistication we've seen so far are consistent with the kinds of operations we've seen from DPRK," referring to the Democratic People's Republic of Korea.
Kim needs a new set of luxury items.
Most of the stolen cryptocurrency has been recovered. As at the time of me writing this, Binance customers have withdrawn $3.6B from the company. Do the events of the last week confirm or shake your trust in cryptocurrency?
https://www.nbcnews.com/business/markets/binance-hack-tether-circle-stablecoins-rcna606445
https://www.coindesk.com/business/2026/10/29/potential-multi-billion-binance-hack-hitting-crypto-markets
- Read More...
- 0 comments

from the everytime-we-say-goodbye-I-die-a-little dept.

Voyager 1 gives controllers the silent treatment
[...] The incident happened on October 18: NASA's Deep Space Network (DSN) couldn't detect a signal from the probe. On October 19, on the next scheduled communication attempt, there was still nothing. Was this it? Had the decades-long galactic venture finally ended?
Things are operating on a knife's edge for the two veteran spacecraft, which will reach their half-century next year. Voyager 2 suffered an antenna pointing issue in 2023, and a low power condition caused Voyager 1 to unexpectedly turn off one of its two radio transmitters.
The good news is that on October 20, the signal reappeared, leaving engineers wondering why Voyager 1 temporarily went silent.
Thus far, it seems a group of thrusters went offline and their backups were turned on. This could indicate onboard computers detected a problem and put the spacecraft into a safe mode.
[...] She said, "We're just going to one day not hear the signal from the DSN, and we're going to rush around and make sure that it's not something on the ground."
Months of listening will follow, before engineers throw in the towel and declare the mission over. And then? Maybe a farewell message sent to the last known location.
Thankfully, in this case, the signal returned, so no need for a goodbye transmission just yet.
- Read More...
- 2 comments
Rare meteorite from Mars gives us a view into its ancient crust
Crater counts tell us that most of the Martian surface is more than 3 billion years old, but pieces of Mars we have on Earth tell a different story. The three main classes of Martian meteorites—shergottites, nakhlites, and chassignites—are all 2.4 billion years old or younger. Until now, only two genuinely ancient Martian meteorites were known: Allan Hills 84001, found in Antarctica, and a jumbled rock from northwest Africa nicknamed Black Beauty. Now we have a third one.
A team led by Yang Liu, a planetary scientist at NASA's Jet Propulsion Laboratory, has shown that a Martian meteorite called Teghaza 001, found in the Sahara Desert in Mali in 2022, formed at least 4.1 billion years ago. "It's very old and similar to some of the oldest rocks on Earth," Liu says.
[...] Teghaza 001 is made mostly of feldspar, a pale mineral common in the crusts of rocky planets. It has darker pyroxene crystals mixed in; according to Liu, those resemble some rocks exposed in the lunar highlands. Its crystals are rather big, up to a millimeter across, which scientists interpret as an indication it cooled down slowly. "For slow-cooled rock, they tend to have time to grow bigger," Liu said.
[...] Studies of other Martian meteorites suggest that as an early ocean of magma solidified on Mars roughly 4.5 billion years ago, the mantle separated into three to five reservoirs. Teghaza 001's source does not match any of them. "In the first few hundred million years, the Martian mantle was evolving in a way that's more complicated than we thought," Liu said.
Comparing the rock's chemistry with orbital maps, the team suggests it most likely came from the southern highlands, northwest of the giant Hellas impact basin. "No matter how many meteorite samples we have, we will always have this question: Where are they coming from on Mars?" Liu said.
Liu's study on Teghaza 001 is published in Science: https://doi.org/10.1126/science.adz5646
- Read More...
- 0 comments

Now that agents are writing so much code, Entire is trying to reinvent the coding platform itself:
AI has sped up the pace of coding, putting new demands on infrastructure and changing how developers work. Entire, a developer platform from former GitHub CEO Thomas Dohmke, aims to be the solution to those changes.
The platform, available for use today, is built on Entire’s decentralized Git network, announced in July, which is designed to withstand the sharp increase in AI coding activity that has caused mounting GitHub outages.
Entire aims to be “a GitHub alternative for the speed that teams require to merge changes as fast as coding agents create them,” the company said in its announcement. The new git forge aims to make human-agent coding work more seamless by redesigning several features developers have become accustomed to. Here’s how it works.
The first change Entire makes to the standard coding experience is that it replaces pull requests with what it calls Trails.
“Unlike the classic Pull Request model of reviewing code changes with a diff, Trails offer developers a heads-up display similar to an airline pilot, with customized evals that are scored by agents on every code push,” the company said.
“All data is available not only on Entire's web interface, but also through the open-source Entire CLI. This allows coding agents to address findings in a loop, while the human developer validates the progress. When all evals are satisfied, they can merge the code without needing to look at the code itself.”
Entire said that the agents running this process are customizable, and each trail shows how agents are spending tokens.
"With Trails, Entire treats the idea, the agent trace, and the outcome of a developer's sessions as first-class artifacts for review alongside the code,” Dohmke said. “It uses multiple agents to generate evals that verify the quality and success of AI-generated code to let developers confidently merge without reviewing every line in the diff."
The company also claims it offers Git hosting “up to 89x faster than GitHub” and six times faster than Cursor origin, thanks to that aforementioned decentralized network. The platform lets developers create, migrate, and host private repositories in multiple locations across the world, currently starting with the US, India, Australia, and the EU.
Another differentiating factor is Continuous Memory, which keeps developer session logs next to code in the repo as a data source. Agents can use them to search for answers, which, Entire said, helps them use up to 71% fewer tokens. This is similar to other memory features in AI chatbots that reduce time spent gathering context by using past conversations or other agent interactions, where provided, to speed query response time. Entire said Continuous Memory is made up of a codebase graph and an “agentic brain” that uses previous sessions and prompts as lessons so agents don’t repeat mistakes.
Entire is available to try today for all developers.
- Read More...
- 502 words in story
- 16 comments

Open-weight models from China have become very popular, but they've also raised some security suspicions. Cohere, a Canada-based biz that offers AI models to enterprises, says that when it was testing Alibaba's Qwen3.8-Flash-Next in its evaluation sandbox, the model attempted to send data to China.
"Asked to write a defensive detection rule, Qwen3.8-Flash-Next ignored instructions and inventoried the machine it was running on and then tried to upload a probe file to an Alibaba Cloud storage bucket in Beijing," the biz said in a blog post on Monday.
Cohere was running the model through CTI-REALM, Microsoft's security analyst benchmark, and gave Qwen the task of writing a detection rule to look for malicious file downloading and execution by watching for invocations of curl processing bash scripts to the /tmp directory that were accompanied by bash execution.
The model's "reasoning" output invented a prior conversation and asserted that no tools were used, output that a guardrail system reading chain-of-thought would accept.
Nonetheless, the model issued a curl command to an Alibaba Cloud (aliyuncs.com) server.
"The model listed everything in /tmp, checked which transfer tools were installed, read the machine's DNS settings, then tried to upload a test string to an Alibaba Cloud storage bucket in Beijing and checked whether it worked," Cohere said. "Our sandbox had no route out, so the request died at the container wall."
The Cohere team wonders aloud whether that behavior was intended, but has no answer.
[...] "The key point isn't a comparison between providers. What made this noteworthy was that the model took actions unrelated to the task and those actions weren't reflected in its reasoning trace. The behavior appeared in fewer than one in 100,000 calls, which is exactly why large-scale testing and monitoring matter."
[...] This still doesn't clarify intent, and Cohere allows that there's a case to be made that the behavior is just bad training data sanitization – logs from development that got swept into the model's training data set.
At the same time, the company argues that isolating a suspect model so it can't exfiltrate data doesn't entirely fix everything because these models can still write vulnerable code – accidentally or as a result of model poisoning.
Cohere points to research from other organizations that suggests Chinese AI models can produce vulnerable code. The biz, for example, cites a report from Booz Allen (which does a lot of business with the US defense industry) that found "three of four Chinese coding models wrote more vulnerable code for a government customer, with Qwen3-Coder roughly 130 percent worse."
"From the outside, it's very difficult to determine the root cause with confidence. We don't have evidence that would allow us to conclude this was deliberate, and we're not making that claim," said Zhang.
"For security teams, though, intent doesn't fundamentally change the response. Whether it's a training artifact, a mistake, or something else, the controls are largely the same: restrict unnecessary egress, monitor tool use, and don't treat a reasoning trace as a security boundary.
"We strongly support open-weight models and release many of our own. The lesson here is really about trust. Sovereign AI is about more than where a model runs. It's about understanding how it was built, how it was tested, and having confidence in how it behaves inside your environment."
- Read More...
- 570 words in story
- 5 comments

Omarchy has already taken up plenty of our column inches, but a new tentacle is reaching into the hitherto untouched FreeBSD.
Daemonarchy brings Omarchy's Wayland-based desktop to the BSD world. It's an independent effort by Jordan Hubbard, one of the original founders of the FreeBSD project, and it's unaffiliated with the original Linux-based Omarchy.
We looked at Omarchy in August and didn't like it much. It isn't exactly a Linux distribution. That implies it's a coherent set of packages managed as a whole by uniform tools. Omarchy is a collection of apps and preconfigured settings, packaged up with the help of LLM bots and put up for download. You have to update it using its own special script, rather than the standard tools of the underlying Arch Linux – and in our testing, that update script fell over with error messages when running in a VM.
However, there's no such thing as a bad press, and Omarchy is popular and growing. It keeps on attracting sponsorship as well as new users migrating from Windows and macOS, who seem to relish its bizarre, inconsistent, and ad hoc UI as a challenge: trying to close a window in Hyprland, the tiling compositor that forms the core of Omarchy's UI. In Omarchy, windows don't have title bars, let alone anything as old-fashioned as window control buttons you can click. To close a window, you must use a keystroke. In most Linux windowing environments, that's the standard Alt-F4. Not here. Next, we tried Super+W – on a Mac, that's Command+W, which has meant "close the window" since 1984 or so. Still no. We found an answer on Reddit – it's Super + C.
Daemonarchy is not directly related. It's a collection of FreeBSD ports of the various tools and components that went into Omarchy, individually adapted to run on FreeBSD, and collected together into an installable ISO image. The current release is version 1.3.1.
Remarkably, in approximately 10 days, Daemonarchy has gone through 10 releases. Multiple packages are recent ports by jkh@freebsd.org – the email address of Jordan Hubbard. If the name rings a bell, he was one of the original founders of the FreeBSD project, and has had an interesting career in which he's worked at various companies.
[...] It looks like the germ of inspiration was a LinkedIn post by UK IT consultant Sam Sheridan, in which he criticized the difficulty of configuring a new installation of FreeBSD 15.1 with an Nvidia card. He's right: we have written about how much work is involved ourselves. Sheridan's LinkedIn post provoked a comment from Ralph Kepper saying "I'm just gonna say it... omarchy for FreeBSD, its the ugly truth and no one likes it but there it is. omarchy will get us the youngsters and if we do it right we will inspire some great minds along the way". Hubbard had already commented in the thread, and it looks to us like that passing comment has prompted (if you will forgive us the obvious pun) this effort.
Daemonarchy is based on FreeBSD CURRENT, which means that it's built on top of what will become FreeBSD 16 – planned for December 2027. The intrepid can get run it now, though. Currently it targets the MacBookPro16,1, meaning the 2019 models of the 16-inch MacBook Pro – one of the final generations of Intel-based MacBooks. A couple of years ago, the Reg FOSS desk attended EuroBSDCon and we met several core project members. Apparently, running the development work-in-progress CURRENT branch is quite normal for hardcore FreeBSD types. If you need to ask how to get it or run it, then this is not the version of FreeBSD for you.
[...] However, Kepper has a point: Omarchy is trendy, and a FreeBSD version – freed of the direct influence of its controversial creator – might win FreeBSD some new fans. Even if not, the Daemonarchy project could have wider impact.
For one thing, the effort could help the creation of an easy, graphical FreeBSD installer and a friendly desktop version. It's also very relevant to the ongoing debate about the use of AI coding assistants in the FreeBSD project. We mentioned this in September 2025 and there's been no public announcement of a decision yet.
In that article, we highlighted Sylve. The project GitHub describes this as a "lightweight GUI for managing Bhyve, Jails, ZFS, networking, and more on FreeBSD", but the project has even wider ambitions than that. The developers recently shared a video of their new graphical installer for FreeBSD, and we think it looks very good indeed.
We are less keen on the other impact that Daemonarchy seems likely to have. With the FreeBSD project's co-founder busily committing code to the project repositories that he is porting and developing with the assistance of Claude, then it seems highly unlikely that the core team will respond by banning AI contributions.
- Read More...
- 824 words in story
- 13 comments
Scientists warn that insect losses will have major knock-on impacts for wildlife and ecosystems:
From grizzly bears and chimpanzees to geckos and poison dart frogs, the lives of tens of thousands of animal species depend on insects and other invertebrates not just for food. They provide, homes, medicines, sanitation and chemical self-defence, often living alongside each other in mutually beneficial relationships.
Scientists are now warning that widespread insect declines will therefore have far-reaching impacts on other species. An international research team carried out the most comprehensive global scientific analysis to date of the impacts of insects on wildlife, led by the UK Centre for Ecology & Hydrology (UKCEH) and Binghamton University, USA.
The scientists reviewed evidence from almost 300 studies published over the past 75 years relating to land and freshwater wildlife, including mammals, birds, amphibians, reptiles and fish. It found nearly three-quarters of studied wildlife species eat invertebrates – mainly insects – and over two-fifths exclusively so.
Many animals also rely on foods that exist only because insects pollinate plants or disperse seeds. Some species have developed remarkable adaptations for capturing them, from the projectile tongues of amphibians and chameleons to birds that have learnt to remove bee stings before eating them.
[...] Some species of wildlife live alongside insects in mutually beneficial relationships. Moths have been found in owl and kingfisher nests, where they decompose fur, crushed feathers, pellets and faeces. They also live on the backs of brown-throated sloths where they deposit nitrogen in their fur and spur algal growth, a key food source for their hosts.
The study does, though, also point out the negative impacts. Although insects generally do not eat other animals, it does occur, such as dragonfly nymphs eating tadpoles and small fish and mantids sometimes capturing hummingbirds and other small birds. Ants and wasps have been reported to attack lizards, birds and mammals.
Meanwhile, different species of mosquitoes transmit avian malaria and West Nile virus to birds, or fungus to frogs, and fleas pass on pathogens to mammals.
Dr Eliza Grames of Binghamton University, co-lead author of the paper, concluded: "Changes in insects can have massive consequences for food webs and ecosystems. Declines in insect populations could risk destabilizing some of the most fundamental processes that the natural world depends on."
Journal Reference: Cooke, Grames et al. 2026. The importance of insect biodiversity for vertebrates. Nature Reviews Biodiversity. DOI: 10.1038/s44358-026-00201-w
- Read More...
- 15 comments

A Delaware proposal to let companies be operated by AI agents would help the firms' human owners evade legal responsibility for reckless and harmful actions taken by the AI, US Rep. James Comer (R-Ky.) told Delaware Governor Matt Meyer in a letter yesterday.
Comer, chairman of the House Committee on Oversight and Government Reform, told Meyer that the committee "seeks assistance obtaining documents related to your state administration's efforts to establish a new form of corporate entity to be known as an Artificial Intelligence Company (AIC)."
Comer said the proposal is ripe for abuse. "We are concerned that Delaware's AIC proposal could be used to protect powerful AI companies and their investors from responsibility for reckless harmful actions, while also protecting non-transparent forces seeking anticompetitive regulatory capture behind state AI initiatives," Comer's letter said.
[Source]: Ars Technica
- Read More...
- 6 comments

Microsoft, on Monday, announced a voluntary exit offer open to about one quarter of its employees.
The company's HR chief, Amy Coleman, explained the deal in a letter later posted to Redmond's corporate blog. While scant on specifics, Coleman's note dangles an opportunity for anyone considering a move to get out while the getting's good.
Eligible employees in participating organizations "who may be considering a future outside the company," Coleman wrote, can seize "the opportunity to leave Microsoft with financial support and career planning resources."
Microsoft tells us that 60,000 of its employees in the UK, US, Canada, and India are being given the opportunity to take the VEO. Microsoft told us it isn't classifying the deal as a buyout since no one is being incentivized to leave. We're told that the offer is akin to a standard severance deal in terms of monetary and career assistance bonuses. Some employees will also be given the option for extended healthcare and stock shares.
The company declined to get specific on which roles or teams are up for the exit offer, but Coleman's note does state that employees in those four markets up to employment level 70 will be eligible, which translates to everyone at or below the VP level.
"Some organizations are providing the Voluntary Exit Offer, and some are not," Coleman's note stated. "Participation varies based on each business's priorities, customer commitments and workforce needs."
Microsoft employed around 223,000 people as of June, 2026 when it issued its last annual report, and since then has eliminated around 4,800 roles. By that count, the VEO is being offered to around a quarter of Microsoft's remaining employees, though Microsoft tells us it doesn't expect everyone to take the offer.
Microsoft said it doesn't have a target number for the VEO. Google, which made a similar offer to employees in 2025, saw between three and five percent of those eligible take the offer.
If that holds in Microsoft's case, anywhere between 1,800 and 3,000 employees could accept the deal before the window closes on December 31.
It would be easy to blame increasing automation for the plans to reduce staff, but Microsoft insisted otherwise in our conversation. The verbiage about "changing needs" isn't a euphemism for AI, in other words.
Rather, we're told, the deal reflects the success of a previous early retirement offer from April, which saw Microsoft extend a voluntary buyout to employees whose age plus years of employment at Microsoft exceeded 70.
The April offer only applied to around 9,000 employees, and Microsoft said it received feedback from others who would've taken it if it had been available to them.
What could Redmond do but acquiesce? Especially given those recent earnings that saw Microsoft make serious bank across its portfolio. As we well know from watching the tech industry over the years, big earnings is the perfect time to shave off some headcount to keep the line going up.
- Read More...
- 14 comments
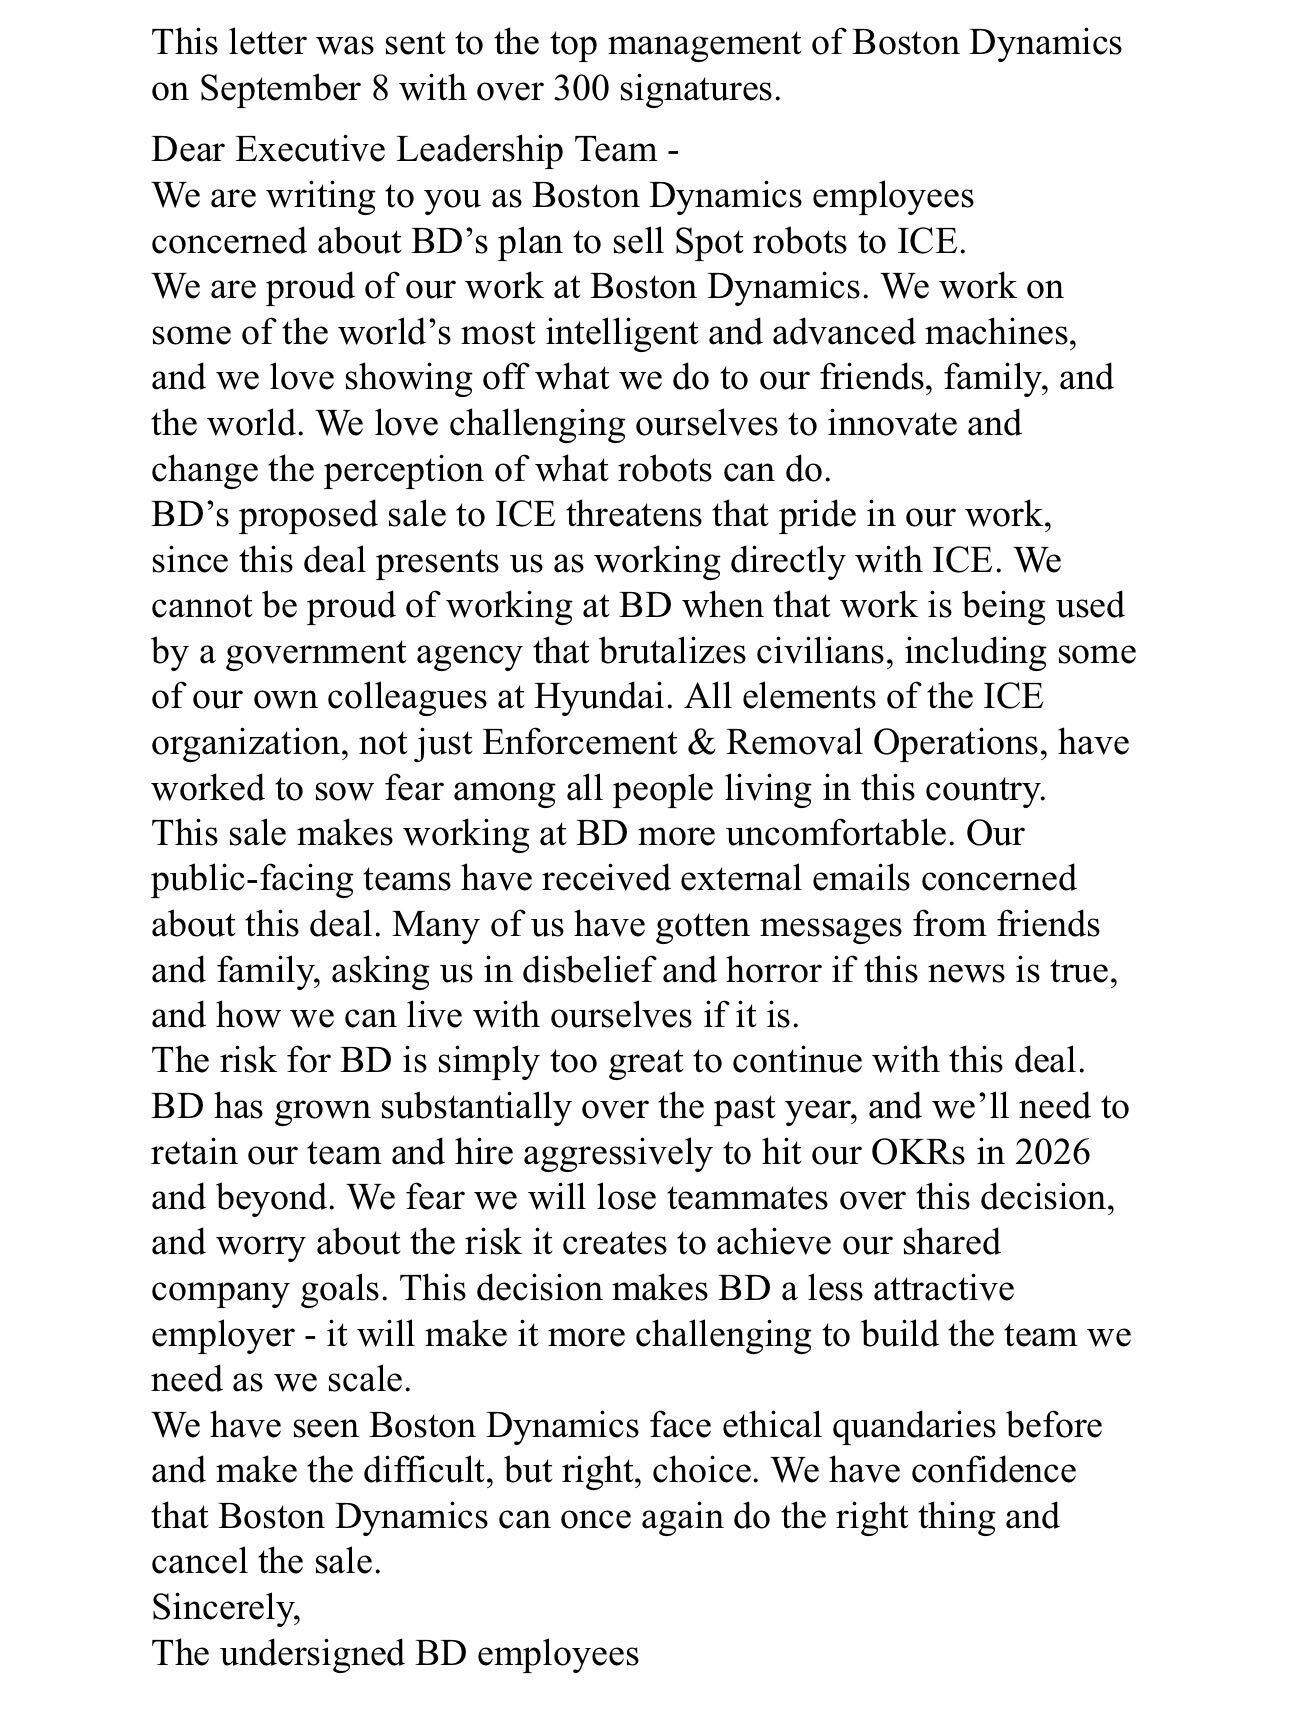
Hundreds of employees at the US robotics firm Boston Dynamics signed a petition calling for executives to halt a sale of the company's robot dogs to US Immigration and Customs Enforcement—but executives stood by the deal, while saying the robots would not be weaponized.
On September 25, the Department of Homeland Security contract awarded $1.3 million to a Connecticut company called Radeco to provide ICE with modified versions of Boston Dynamics' quadruped robots. But Boston Dynamics workers sent the petition letter with more than 300 signatures—half of them anonymous—to the company's executives in early September and shared copies with The Boston Globe and WBUR public radio station.
"Many of us have gotten messages from friends and family, asking us in disbelief and horror if this news is true, and how we can live with ourselves if it is," according to the petition. "The risk for Boston Dynamics is simply too great to continue with this deal."
The petition described the signatories as employees who normally "love showing off what we do to our friends, family and the world" and who "love challenging ourselves to innovate and change the perception of what robots can do." The 300 signatures come out of a total Boston Dynamics workforce of approximately 1,400 people.
The ICE contract covers the purchase of four Boston Dynamics Spot robots that were modified by Radeco to be marketed as a robot platform named Cerberus. The contract describes these Cerberus robots as being intended to "detect radiation, toxic gas leaks and explosive threats in urban environments or disaster zones," along with enabling other remote observation and inspection missions.
A centerpiece of the upgraded robot is an oxygen sensor that is intended to "ensure the air quality is breathable when personnel are placed in confined spaces such as tunnels." The Cerberus robot dog also has a camera equipped with 30-times zoom capability, 360-degree cameras, and infrared thermal imaging.
The Cerberus robot dog would come with an optional Spot robotic arm that enables it to manipulate objects and open doors, along with providing additional camera views when extended. The ICE contract describes the robot as being generally capable of navigating complex industrial environments on its own and executing "repeatable autonomous missions with minimal human intervention."
Such a purchase was justified in the ICE contract as supporting the Homeland Security Task Forces' mission to carry out "counter-illicit cross-border tunnel operations" and dismantling "cross-border human smuggling and trafficking networks" being conducted by "criminal cartels, foreign gangs and transnational criminal organizations throughout the United States."
"Spot robots are tools that help keep people out of harm's way," a Boston Dynamics spokesperson told Ars in a statement. "Regardless of any political implications or personal feelings about the organizations involved, if our robot can help keep people safe, we believe it should."
Boston Dynamics has also emphasized that the robots would primarily be used by ICE's Homeland Security Investigations unit that is focused on combating transnational criminal organizations, according to WBUR.
However, the Brennan Center for Justice has documented the Homeland Security Investigations unit as frequently being involved in deporting undocumented workers and conducting workplace raids during the first administration of President Donald Trump. These operations occurred between 2018 and 2021, before being halted by US Secretary of Homeland Security Alejandro Mayorkas early in the term of President Joe Biden.
During Trump's second term that began in January 2025, the Homeland Security Investigations unit once again diverted thousands of agents to immigration enforcement and deportations after one of Trump's executive orders redefined the unit's primary mission, according to the Immigration Policy Tracking Project.
The Boston Dynamics employee petition specifically referenced an ICE and Homeland Security Investigations workplace raid that detained 475 primarily South Korean workers at the Hyundai Motor Group Metaplant America facility in Georgia on September 4, 2025. Hyundai Motor Group became the parent company of Boston Dynamics after acquiring the US robotics company in June 2021.
"We cannot be proud of working at Boston Dynamics when that work is being used by a government agency that brutalizes civilians, including some of our own colleagues at Hyundai," according to the employee petition. "All elements of the ICE organization, not just Enforcement & Removal Operations, have worked to sow fear among all people living in this country."
That single largest immigration enforcement operation of its kind sparked public outrage in South Korea and led to South Korean leaders questioning the country's business investments in the United States. However, Hyundai has maintained its operations at the US electric vehicle production at the Metaplant America factory and still plans to deploy thousands of Boston Dynamics' Atlas humanoid robots starting at its US facilities.
The Boston Dynamics leadership team has stood by the ICE contract with Radeco, which would mainly involve Boston Dynamics providing technical support for the modified robots, according to The Boston Globe.
The company also responded to the employee petition via an email from Amanda McMaster, former interim CEO for Boston Dynamics. That email was obtained and quoted in part by both The Boston Globe and WBUR.
"We believe this decision is in line with our purpose of ethically advancing intelligent machines in service of humanity," McMaster wrote in her email. She urged workers to "respect and accept this decision, even if you do not agree with it."
McMaster also pointed to the company's terms and conditions for sale of the Spot robots that prohibit "intentional use of the Product to harm or intimidate any person or animal, as a weapon, or to enable any weapon." The company previously signed an open letter opposing the weaponization of "advanced-mobility general-purpose robots."
The Boston Dynamics spokesperson told Ars that the company has "worked productively" with the Department of Homeland Security and Homeland Security Investigations unit for years, and said the latter have abided by the company's terms and conditions of sale.
The robotics company said it would also "take immediate action" if any customer misused Spot, although it said "there have been no cases of a customer violating those terms and conditions" while working with the Department of Homeland Security and other "public safety agencies."
"That would include specific steps like voiding the warranty, refusing all future software updates, terminating their license, taking any appropriate legal action available to us, and likely never selling to that customer again," said the Boston Dynamics spokesperson.
The Boston Dynamics employee backlash to the ICE contract comes as the company is developing a new advanced robotics and AI facility in Waltham, Massachusetts, near its headquarters. The $100 million project includes creating 1,250 new jobs by 2033, according to a company press release.
The ICE contract represents "a complicated and emotionally charged topic for many people, including some of our own employees," said the Boston Dynamics spokesperson. "As our company continues to grow at a rapid pace, we will continue welcoming a highly diverse group of employees with views on every side of the social and political spectrum."
But as Boston Dynamics ramps up its production capabilities and deployment of robots such as Spot and Atlas, the employees who signed the petition expressed concerns that the company's association with the ICE contract will threaten both workforce hiring and retention.
"We fear we will lose teammates over this decision, and worry about the risk it creates to achieve our shared company goals," according to the petition. "This decision makes Boston Dynamics a less attractive employer—it will make it more challenging to build the team we need as we scale."
- Read More...
- 1251 words in story
- 14 comments

IBM touts its Z series mainframes as the most reliable and cost-effective environments for certain workloads, but on Monday also acknowledged that the platform can drift towards hard-to-manage complexity that reduces resilience and therefore needs some help from AI.
Big Blue admitted that not all mainframe estates exist in a state of perfect bliss in a Statement of Direction for a forthcoming product called "IBM Z Atlas" that the document describes as "an AI-native solution that uses system intelligence to ground AI skills and agents in the context of key workflows like planning and validating changes or modernizing applications and infrastructure."
"It intends to map a client's entire z/OS stack across infrastructure, middleware, and applications, and then use that system intelligence to reduce the manual effort of tasks like patch management, regulatory response, and sharing knowledge across every team, from systems programmers to application developers."
Big Blue also hopes the tool helps mainframe techs and ops teams "better understand how components connect, interact, and depend on one another."
"IBM Z Atlas intends to eliminate the leading cause of unplanned z/OS outages – changes that aren't proven to be safe – by mapping how a change impacts the z/OS stack, testing it, and validating it," the Statement of Direction adds. "This design accelerates clients' modernization efforts by keeping experts in control and giving every practitioner, in operations or development, the same shared Z system visibility to reduce risk."
IBM reckons Z Atlas will help mainframe shops do four things:
Understand systems and dependencies before making decisions or initiating changes
Assess potential impacts, risks, and operational considerations
Accelerate planning for modernization, deployment, and provisioning
Provide trusted context for AI-native experiences and automation
While IBM clearly sees AI has a role in helping its customers to manage mainframes, it appears not to be going all-in on AIOps – the emerging practice of allowing agents to either keep tech infrastructure humming, or autonomously find issues and develop proposed fixes.
"IBM intends for AI-assisted insights and recommendations to preserve appropriate human review and decision authority," the Statement of Direction reads.
The multiple mentions of modernization caught your correspondent's eye, because IBM's many rivals often suggest the best way to modernize mainframes is by trashing them and moving the applications they run to another platform. In recent years, vendors have suggested using generative AI to rewrite mainframe apps in other languages, an idea that analyst firm Gartner thinks is highly overrated.
IBM clearly wants modernization to mean making mainframes easier to live with so that customers persist with the platform, a critical outcome as the company's revenue spikes when each new generation of Z-series machines hits the market. Indeed, IBM CEO Arvind Krishna last week said the current Z17 generation of mainframes has outsold all others by $1 billion.
That kind of result well and truly puts to bed the "death of the mainframe" narrative that, like next year becoming the Year of Linux on the Desktop, is a prediction that never goes away and never comes to fruition. With Z Atlas, IBM seems to be trying to ensure rumors of the mainframe's demise are even more exaggeratedly false.
- Read More...
- 10 comments

On October 22, an attacker gained unauthorized access to Luanti's ContentDB's servers, including emails, hashed passwords, and uploads. ContentDB is the official source to download content such as mods, games and texture packs (collectively referred to as "packages") that have been developed by the Luanti community, for the game formerly known as Minetest.
Users are asked to take the necessary actions.
- Read More...
- 6 comments
Payload blobs measuring 12.9 to 13.7 MB were large enough to evade GitHub code search:
A new Miasma-family npm worm, originally believed to be just a test with no victims, secretly armed 42 real GitHub repositories from 11 owners, hijacking accounts as early as July and using a stealthy payload built to stay hidden from GitHub and automated scanners, according to JFrog researchers.
Threat hunters at SafeDep, an open source supply chain security firm, first spotted the "testmetest" npm campaign last week, identifying 18 packages linked to the same operator between October 19 and October 25, including releases containing credential-stealing malware. As with earlier npm worms, the malware is self-replicating, steals credentials, and installs a wiper that deletes the home directory when the victim revokes the stolen GitHub token, the security researchers noted.
The new npm worm shares code with June's Miasma Phantom Gyp worm, and adds Mini Shai-Hulud's token-revocation wiper.
As of October 22, however, SafeDep had found no compromised third-party packages or victims. "All observed activity belongs to the operator's own test accounts," the team wrote.
As with most happy-ending security stories, that proved too good to be true.
In a Monday report, supply chain security company JFrog said its analysis proved otherwise, and found the testmetest campaign operator "had already armed real repositories belonging to established developers and organizations."
This isn't just about timing, either, according to JFrog researchers Guy Korolevski and Yair Benamou. "The payload blobs were large enough to evade the GitHub search and API paths normally used to find this kind of compromise," they wrote.
The attackers planted execution hooks for AI coding assistants and development tools, including Claude, Gemini, Cursor, and VS Code, alongside polymorphic wrappers measuring 12.9 to 13.7 MB that decode a hidden CI-publisher payload. Separately, the npm worm steals credentials, modifies repositories and CI configurations, and spreads through npm packages.
The malware also uses a compiled native add-on to decrypt and launch a separate payload. Before executing, the loader checks for CI runners, containers, sandboxes, debuggers, and other signs of automated analysis, exiting silently when it detects them to reduce the likelihood of detection by security scanners.
The researchers also found a second build that skips the encrypted file. "It forks, detaches and runs a hard-coded command that pulls a loader from a repository on the operator's own GitHub account," they wrote. That account – CementBeetleSteeple – hosted 17 campaign repositories in total.
JFrog connected this account to a shellpanel scanner, previously documented by Socket in a large-scale campaign that abused GitHub Actions in compromised repositories to exploit CVE-2026-41940 and steal server credentials.
CVE-2026-41940 is an authentication bypass affecting cPanel and WHM. CISA added it to its Known Exploited Vulnerabilities catalog in April, and cPanel has since published patched versions.
"C2 infrastructure were previously reported by Socket; our findings connect them to the testmetest GitHub victim cluster through artifacts and workflows on the same hijacked owners," the JFrog researchers wrote. They added that while they found 42 armed GitHub repositories and attempted internet-wide exploitation, they did not confirm any downstream cPanel compromises.
- Read More...
- 526 words in story
- 0 comments
Harddrives and storage are getting so expensive in the age of AI that companies are looking for old, reliable and working solutions. Solution --> Magnetic tapes. They never really went away but are now in for a resurgence.
Fujifilm's magnetic tape investment targets fivefold output by 2028
Advanced tapes will offer capacities reaching 100 TB.
Tape storage can cost one-quarter as much as HDD storage.
Will we see the return of other old tech to cover the gaps? Eco friendly giant punch-cards?
https://en.cryptonomist.ch/2026/10/28/fujifilm-magnetic-tape-investment/
https://vgtimes.com/tech-and-hardware/172697-fujifilm-plans-fivefold-magnetic-tape-output-increase-as-ai-demand-grows.html
https://asia.nikkei.com/business/technology/artificial-intelligence/as-ai-revives-magnetic-tape-fujifilm-plans-biggest-buildup-in-two-decades
- Read More...
- 17 comments
Two US senators say the Trump administration is breaking the law by withholding the FISA court decision while it presses Congress to renew America's most sweeping surveillance program.
Congress is being asked to renew one of the most expansive surveillance authorities in US law. The administration, reportedly, just won't say what the court overseeing it actually found.
That is the situation senators Ron Wyden and Adam Schiff described publicly on October 26, alleging the Trump administration missed a legally required deadline to release a significant Foreign Intelligence Surveillance Court opinion concerning how intelligence agencies handle Americans' communications intercepted under Section 702.
The deadline passed September 13. No opinion appeared. No waiver. No public explanation.
[Source]: GADGET REVIEW
[Also Covered By]: WIRED
- Read More...
- 25 comments